TL;DR

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
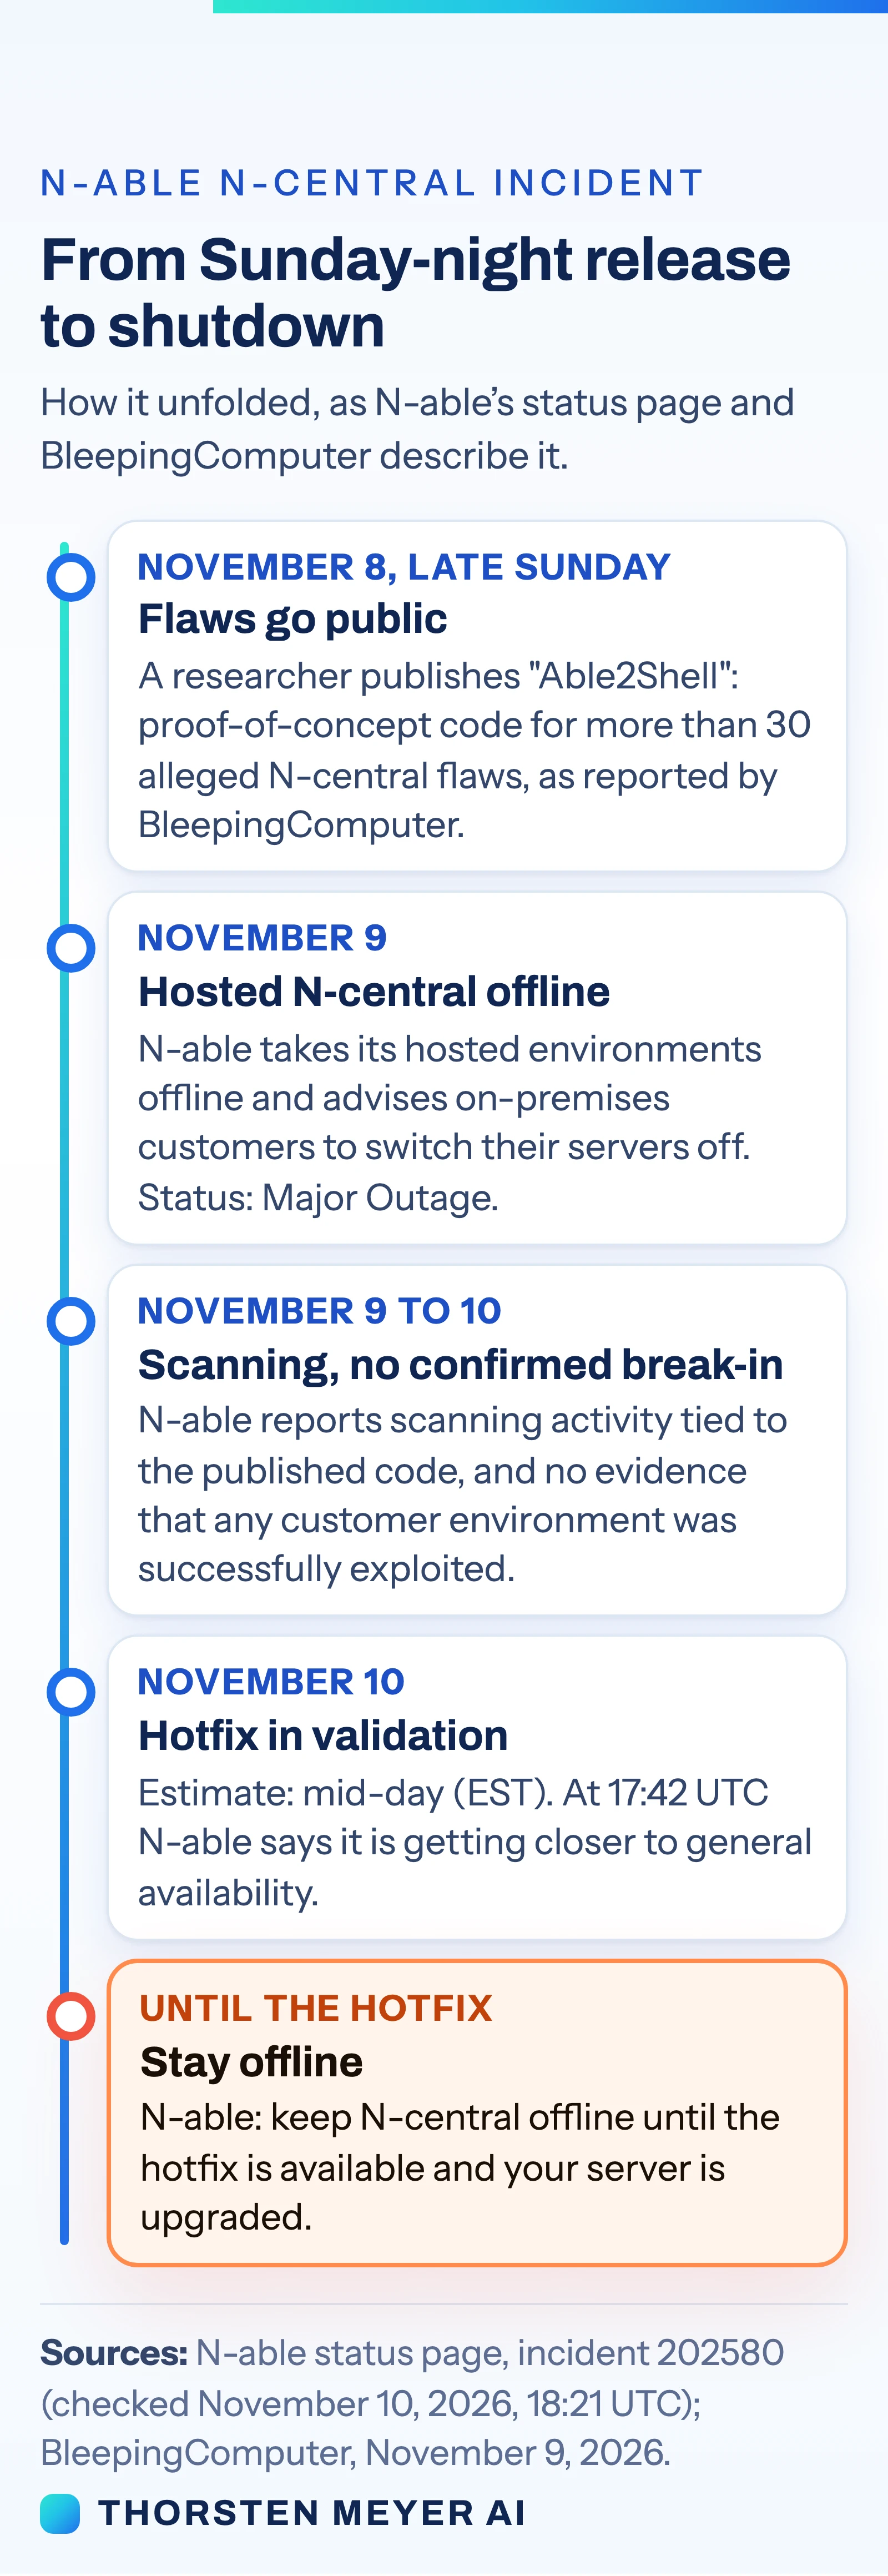
N-able took its hosted N-central service offline on November 9, 2026, and urged customers running it on their own servers to disconnect those systems after exploit code for more than 30 alleged flaws was published. The company reported scanning linked to the code but said it had no evidence of successful exploitation; a fix had not been announced by 19:37 UTC on November 10.
N-able took its hosted N-central environments offline on November 9, 2026, and urged customers running the remote management platform on their own servers to disconnect them after a researcher published exploit code for more than 30 alleged vulnerabilities. The shutdown affects IT providers that use N-central to manage client devices and networks; N-able said it had seen related scanning but had no evidence of successful exploitation.
N-able described the disclosure as “non-responsible communication of critical vulnerabilities.” On its status page, the company said it had taken hosted environments offline as a precaution while it worked to secure them and prepare remediation. Hosted customers could not access the classic environment, and associated services might also be unavailable. N-able advised customers with on-premises servers to take them offline and keep them offline until the company confirmed they could safely return.
BleepingComputer reported that a researcher published a GitHub repository called Able2Shell late on November 8 with proof-of-concept exploits for more than 30 flaws. The Hacker News reported a count of 33. BleepingComputer said the researcher tested the flaws against a pre-release build, N-central Appliance 2026.4.0.31, and believed most or all might also affect earlier versions. That assessment has not been independently established in the material available.
N-able’s status page listed a major outage affecting hosted and on-premises N-central in the Americas, Asia-Pacific and Europe. The company’s latest update cited in the source, posted at 17:42 UTC on November 10, said it was “getting closer to making the release generally available this afternoon.” By 19:37 UTC, N-able had not announced that release.
Why N-central Outages Reach Clients
N-central is a remote monitoring and management platform used by managed service providers and IT teams to oversee customer devices and networks. Tools of this kind can let providers install software, run scripts, apply patches and access systems remotely. As a result, an exposed management server can affect more than the organization that operates it: a provider may use one system to manage many clients.
Security firm Field Effect has said that a compromised N-central server could give attackers a path to downstream systems. That is a risk description, not evidence that attackers used these newly disclosed flaws to enter customer networks. N-able’s reported lack of evidence of successful exploitation is the company’s assessment at the time of its update; the shutdown and continued investigation show why providers and customers need to establish whether any systems were exposed.
The immediate effect is operational as well as security-related. Providers may lose access to a central tool for routine monitoring and support while it is offline. Customers should ask their IT provider which management services are affected and how urgent support, patching and other work will be handled during the outage.
Products Worth Considering

Amazon Kindle Scribe (3rd Generation), 64GB, 11-inch Display, Graphite, with Premium Pen

Bose Lifestyle Ultra Compact Wireless Smart Home Speaker Bundle, Black

Samsung Galaxy Tab S7 11-inch Android Tablet 128GB Wi‑Fi with S Pen Mystic Black
As an affiliate, we earn on qualifying purchases.
Earlier N-central Security Entries
The latest disclosure comes amid earlier N-central entries in the U.S. Cybersecurity and Infrastructure Security Agency’s Known Exploited Vulnerabilities catalog. According to the source material, a version of the catalog checked on November 9 listed five N-central entries. Three were added in 2026: CVE-2026-18577 and CVE-2026-18556, described as authentication bypass flaws, and CVE-2026-86218, which CISA says could allow pre-authentication remote code execution. CISA noted that CVE-2026-18577 resulted from an incomplete patch for CVE-2026-18556. Two other listed entries date to August 2025.
Those catalog entries concern previously identified vulnerabilities. They provide relevant history about security issues in the product, but they do not establish that the flaws in the Able2Shell release are valid, affect the same versions, or have been exploited.
““As a precautionary measure, we have temporarily taken our Hosted N-central environments offline while we take the necessary actions to secure the environments and implement appropriate remediation.””
— N-able, in its status page update
Scope and Exposure Remain Unclear
Several key points were unresolved as of the latest time in the source material. It was not established whether all the published flaws are valid, which product versions are affected, or whether systems were accessed before N-able’s shutdown guidance. The researcher reportedly tested a pre-release version and believed earlier versions might also be affected; that remains an attributed assessment rather than a confirmed version list.
N-able said it had observed scanning associated with the published proof-of-concept code, but reported no evidence that a customer environment had been successfully exploited. The source material does not establish how broad that scanning was, whether any attempted access succeeded, or whether all customer environments have been examined. A safe return-to-service time was also not yet confirmed.
Awaiting N-able’s Release Guidance
N-able’s next stated step was to make its remediation release generally available and provide further guidance on when on-premises servers could safely come back online. As of 19:37 UTC on November 10, that release had not been announced. Customers and service providers should follow N-able’s status page and direct instructions, and confirm with their provider which systems and services are affected before restoring access.
Further updates should clarify the affected versions, the remediation steps, and whether N-able has found evidence of successful exploitation. Until the company provides its return-to-service guidance, the status of individual hosted and on-premises environments remains subject to change.
Key Questions
Why did N-able take N-central offline?
N-able said it took hosted environments offline and advised on-premises customers to do the same after a researcher published exploit code for more than 30 alleged vulnerabilities. The company said the steps were intended to secure environments and support remediation.
Were N-central customers successfully hacked?
N-able said it had seen scanning activity associated with the published proof-of-concept code but had no evidence of a successfully exploited customer environment. The source material does not independently establish whether any intrusion occurred.
Which N-central versions are affected?
The source material does not provide a confirmed affected-version list. BleepingComputer reported that the researcher tested a pre-release build and believed most or all flaws might affect earlier versions; that assessment has not been confirmed by N-able in the cited updates.
When can on-premises servers come back online?
N-able had not confirmed a safe return time by 19:37 UTC on November 10, 2026. Its guidance was to keep on-premises servers offline until it provided further instructions.
Source: Thorsten Meyer AI