
TL;DR

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
DMARC is an email authentication protocol that helps prevent domain spoofing and phishing attacks. However, it does not protect against all email-based threats. This article explains what DMARC does and its limitations.
DMARC (Domain-based Message Authentication, Reporting, and Conformance) is confirmed to be an effective tool in reducing email spoofing and phishing attempts when properly implemented. However, it does not provide complete protection against all email threats, such as malware delivery or social engineering attacks, according to cybersecurity experts.
DMARC works by allowing domain owners to specify how receiving mail servers should handle unauthenticated emails that claim to originate from their domain. You can learn more about DMARC enforcement and best practices. When correctly configured, it helps prevent malicious actors from forging sender addresses, thereby reducing phishing and brand impersonation.
Current industry data shows that organizations with DMARC policies in place experience fewer successful spoofing attacks. Implementing DMARC correctly is crucial, especially since many domains still lack enforcement. Email security vendors emphasize that DMARC, combined with SPF (Sender Policy Framework) and DKIM (DomainKeys Identified Mail), significantly enhances email authenticity verification.
However, experts note that DMARC does not block all types of email threats. To improve your email security posture, consider reviewing your domain authentication policies and enforcing DMARC policies more strictly. It does not prevent malware-laden attachments or links embedded in emails, nor does it stop social engineering tactics that trick users into revealing sensitive information. Additionally, some malicious actors may bypass DMARC protections by exploiting vulnerabilities in other parts of the email delivery chain.
Why DMARC Implementation Is Crucial for Email Security
Understanding DMARC’s capabilities helps organizations and individuals better defend against email-based fraud. While it reduces the risk of domain spoofing, relying solely on DMARC leaves gaps that cybercriminals can exploit. Proper deployment of DMARC, alongside other security measures, is essential for comprehensive protection.
Products Worth Considering

Sony WH-1000XM6 Wireless Noise-Canceling Over-Ear Headphones, Blue, Bundle
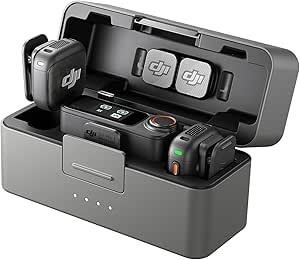
DJI Mic 3 Wireless Microphone System (2 Transmitters, 1 Receiver, Charging Case)

Bose QuietComfort Wireless Bluetooth Headphones with Active Noise Cancellation, Mic, USB‑C Charging, Deep Bass, 24‑Hour Battery – White Smok
As an affiliate, we earn on qualifying purchases.
DMARC’s Role in the Broader Email Security Ecosystem
Introduced in 2012, DMARC has become a standard component of email authentication strategies. Its adoption has grown among major corporations and government agencies aiming to protect brand reputation and prevent phishing. Despite its effectiveness, DMARC is only one part of a layered security approach, which includes user training, anti-malware solutions, and ongoing monitoring.
Recent reports indicate that while DMARC adoption is increasing, many domains still lack proper configuration, reducing its overall effectiveness. Cybersecurity incidents continue to highlight the need for multifaceted defenses against evolving email threats.
Unconfirmed Aspects of DMARC’s Effectiveness and Limitations
While experts agree on DMARC’s role in preventing domain spoofing, the extent of its effectiveness across different industries and attack types remains somewhat uncertain. There is ongoing debate about how well DMARC performs when not properly configured, and how quickly organizations adopt best practices.
Additionally, it is not yet clear how emerging email threats, such as AI-generated phishing or sophisticated malware, will impact DMARC’s protective capabilities in the future.
Next Steps for Enhancing Email Security with DMARC
Organizations should prioritize proper DMARC configuration and monitor reports to improve effectiveness. Experts recommend integrating DMARC with other security measures, including user training and advanced threat detection systems.
Industry groups are also working on developing standards and best practices to address current gaps. Future developments may include more automated tools for configuration and real-time threat response.
Key Questions
Can DMARC prevent all types of email attacks?
No, DMARC primarily prevents domain spoofing and phishing that relies on forging sender addresses. It does not block malware, malicious links, or social engineering attacks that do not depend on spoofed domains.
How can organizations improve their DMARC setup?
Organizations should ensure they publish strict DMARC policies, monitor aggregate reports regularly, and implement SPF and DKIM correctly. Consulting security experts for configuration helps maximize protection.
Is DMARC effective against AI-generated phishing emails?
DMARC can help identify spoofed domains but does not detect AI-generated content or highly targeted social engineering. Additional security layers are needed to address these evolving threats.
What are the risks if an organization does not implement DMARC?
Without DMARC, organizations are more vulnerable to email spoofing, which can lead to brand damage, phishing attacks, and data breaches. Implementing DMARC reduces these risks but does not eliminate them entirely.
Source: hn