Memory forensics is vital for investigating attacks in RAM. It helps you uncover volatile data like active processes, network connections, and even malware remnants. By quickly capturing memory, you can spot anomalies and understand how attackers gained access. It also reveals insights into the broader threat landscape, especially with cloud storage exploitation. You’ll find that analyzing user interactions is key in reconstructing attack timelines and developing targeted response strategies. There’s so much more to explore on this topic.
Listen free for 30 days with Audible
Thousands of audiobooks and originals — cancel anytime.
As an affiliate, we earn on qualifying purchases.
Key Takeaways
- Memory forensics uncovers volatile data in RAM, revealing temporary processes and network connections vital for understanding attacks.
- Rapid memory acquisition tools capture critical evidence before it’s lost, aiding in real-time investigations.
- Analyzing memory can expose malware that evades traditional disk detection, providing essential clues for threat assessment.
- Investigating user interactions and sessions helps reconstruct attack methods and timelines, clarifying how breaches occurred.
- As cloud storage usage grows, memory forensics identifies data exfiltration tactics and cloud applications involved in attacks.
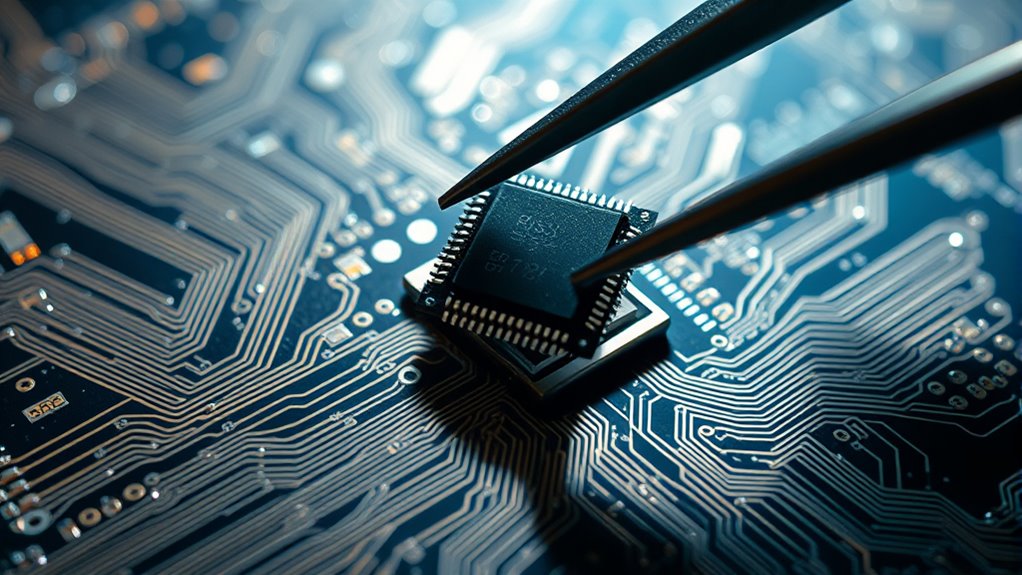
Memory forensics, while often overlooked, plays a critical role in uncovering digital evidence from volatile memory. When you’re faced with a security incident, the data stored in RAM can reveal essential insights that might not be available elsewhere. You might not realize it, but RAM holds temporary data that can include running processes, network connections, and even fragments of malware. This information can be a goldmine for understanding how an attack unfolded and, more importantly, how to prevent future incidents.
Memory forensics is crucial for revealing insights from volatile RAM that can help prevent future security incidents.
During an investigation, you’ll want to focus on capturing the memory of a compromised system as quickly as possible. This is where tools for memory acquisition come into play. These tools let you extract the contents of RAM, allowing you to analyze it for signs of malicious activity. One of the first things you should check for is malware. By inspecting the active processes and loaded modules, you can identify any unauthorized software that may be running. Malware detection in memory is essential because it often behaves differently in RAM than it does on disk. You might find remnants of malware that were designed to evade traditional detection methods.
Furthermore, the interplay between memory forensics and cloud storage can’t be overstated. As more organizations shift to cloud environments, understanding how data flows between local systems and the cloud becomes indispensable. You should consider how an attacker could exploit cloud storage to exfiltrate data or maintain persistence in a compromised system. By analyzing memory, you can often find traces of cloud-based applications that may have been used during an attack, giving you a clearer picture of the threat landscape. Utilizing techniques from waterless planters can help maintain system performance while monitoring for potential threats.
Another important aspect of memory analysis is tracking user interactions. By examining user sessions and opened files, you can gather context around the attack. This can help you determine whether the threat actor gained access through phishing, exploitation, or another method. The more you understand about these interactions, the better equipped you’ll be to respond effectively.
Frequently Asked Questions
What Tools Are Commonly Used for Memory Forensics Investigations?
For memory forensics investigations, you’ll commonly use tools like Volatility and Rekall. These tools enable you to conduct volatile analysis, allowing you to extract valuable information from RAM. You can also use tools like WinDbg for kernel analysis, which helps you dive deeper into system-level processes. By leveraging these tools, you can uncover hidden threats and gather essential evidence to understand the attack better.
How Does Memory Forensics Differ From Traditional Disk Forensics?
Memory forensics dives into the volatile data swirling in a computer’s RAM, capturing ephemeral information like a snapshot of chaos in real time. Unlike traditional disk forensics, which sifts through static data like a meticulous librarian, memory forensics uncovers fleeting secrets that vanish in an instant. You’re not just examining files; you’re unraveling active processes, network connections, and user activity that paint a vivid picture of what’s happening right under your nose.
Can Memory Forensics Recover Deleted Files?
Yes, memory forensics can help recover deleted files, but it has its limitations. You’re dealing with volatile data, which means it’s temporary and can disappear quickly. When you analyze the RAM, you might find remnants of deleted files that were in use before shutdown. However, if the data’s been overwritten, recovery becomes more challenging. Still, it’s a powerful tool for uncovering information that traditional methods might miss.
What Types of Malware Can Be Detected Through Memory Forensics?
You can detect various types of malware through memory forensics, including live malware and rootkits. While some malware hides in files, others lurk in RAM, waiting for the right moment to strike. Using memory analysis, you uncover these threats, revealing their behavior and persistence. Identifying these malicious programs allows you to neutralize them swiftly, ensuring your system remains secure. By understanding their tactics, you can create a more robust defense against future attacks.
How Long Does a Memory Forensics Investigation Typically Take?
A memory forensics investigation typically takes anywhere from a few hours to several days, depending on the complexity of the case and the amount of RAM analysis required. You’ll find that simpler cases might wrap up quickly, while those involving advanced malware or extensive data can extend the investigation timeline considerably. Staying organized and focused can help streamline the process, ensuring you gather all necessary information efficiently.
Conclusion
In the world of cyber security, many believe that once an attacker has left the scene, the evidence disappears. But that’s not true. Memory forensics reveals hidden clues in RAM, allowing you to uncover malicious activities even after a breach. By understanding the intricacies of RAM and how attackers operate, you can turn the tables and catch them red-handed. So, don’t underestimate the power of memory; it just might hold the key to your next big breakthrough.
College move-in / dorm season Picks
dorm essentials
As an affiliate, we earn on qualifying purchases.