TL;DR
CISA urged organizations on November 17, 2026, to patch Java4Shell, a memory-corruption flaw in Java’s Base64 decoder that could enable remote code execution under specific conditions. The affected runtime, processor and input path must all be present; CISA’s record listed no exploitation, and the flaw was not in its known exploited vulnerabilities catalogue as of November 18.
The U.S. Cybersecurity and Infrastructure Security Agency urged organizations on November 17 to patch CVE-2026-114938, a memory-corruption flaw in an optimized Base64 decoder in the Java HotSpot virtual machine. CISA says specially crafted input could crash the JVM and allow unauthenticated remote code execution, but exposure depends on the Java runtime, processor and how outside data reaches the decoder.

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
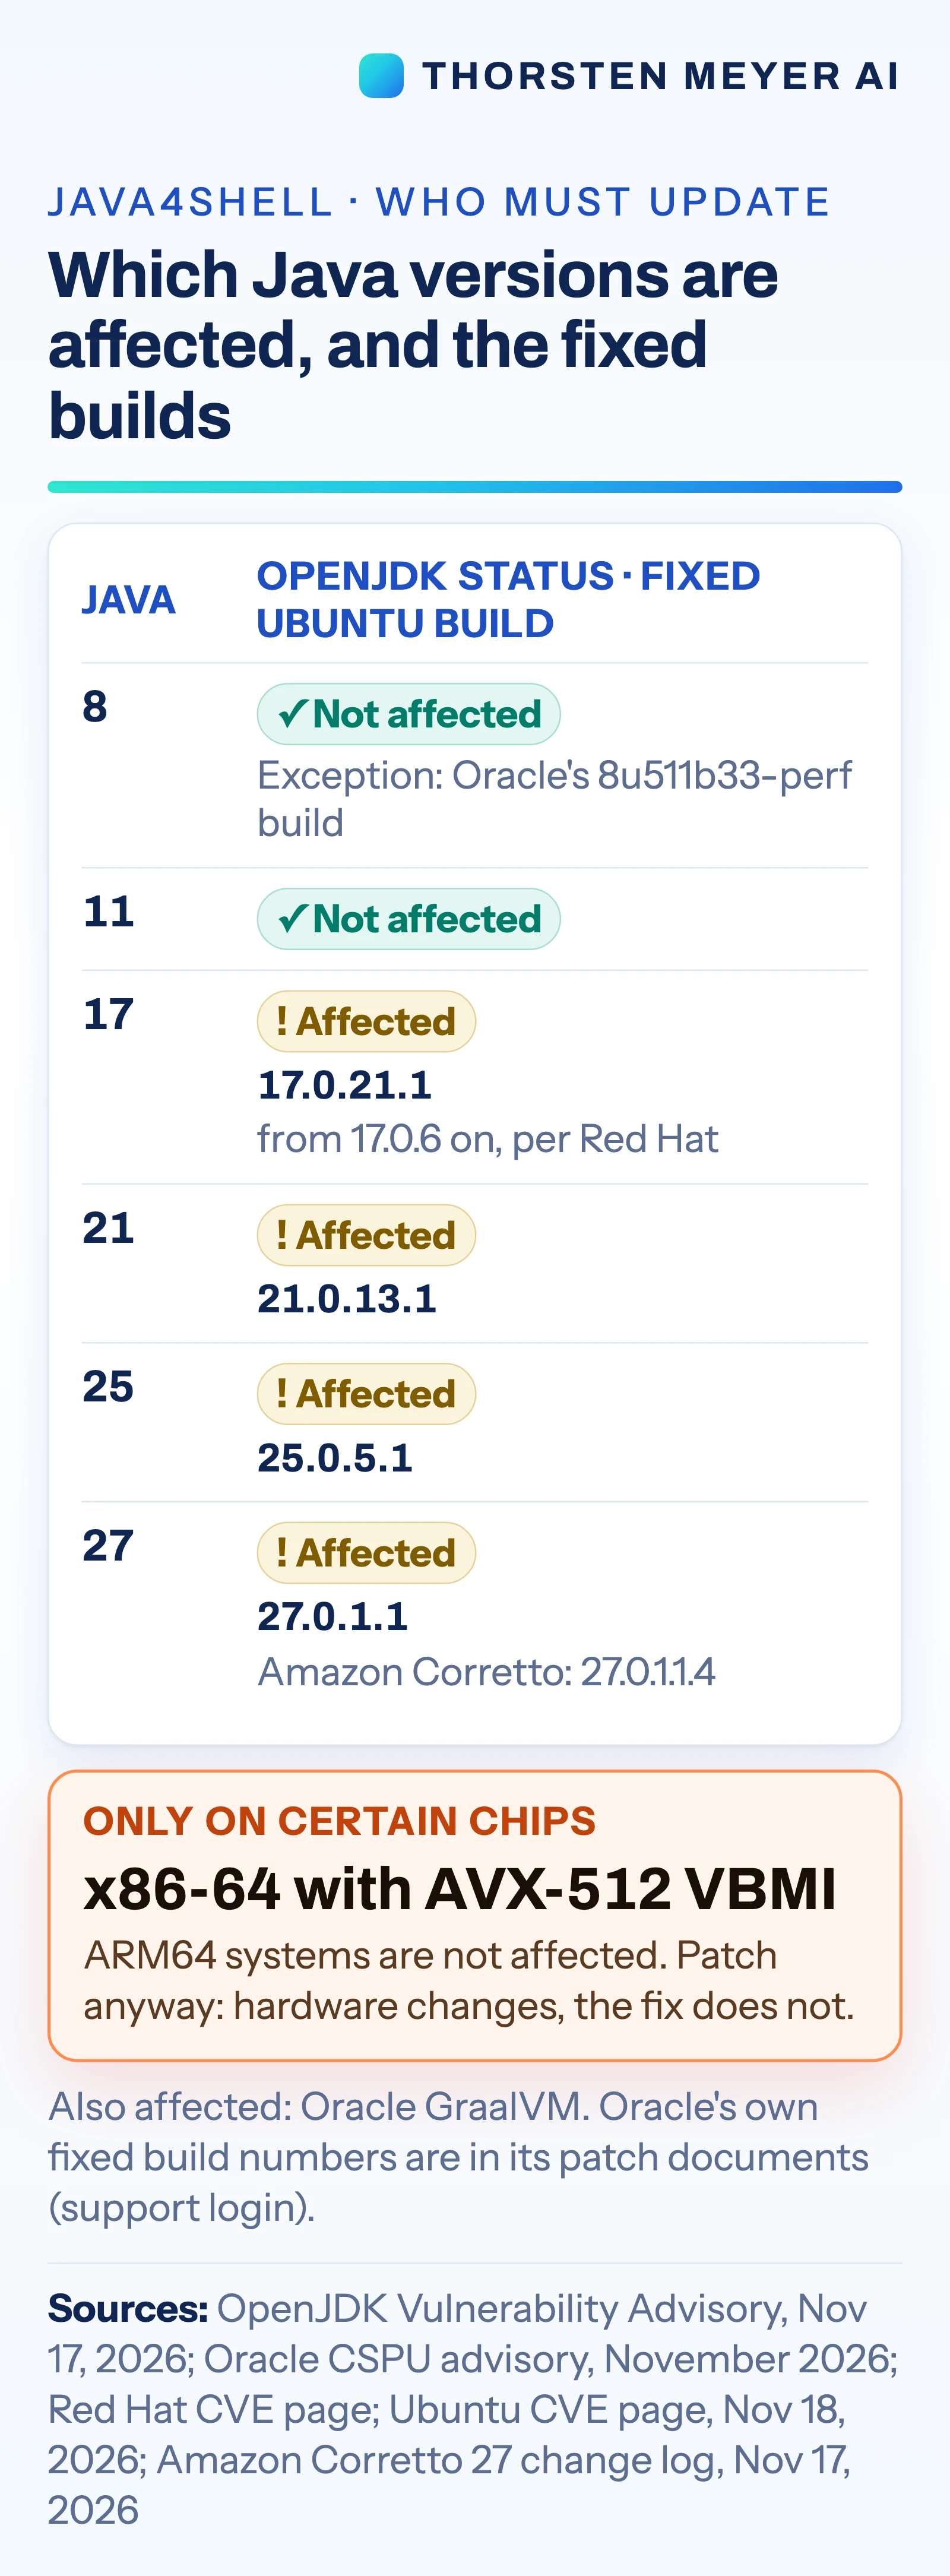
The vulnerability, called Java4Shell by its finders, affects Java 17, 21, 25 and 27 runtimes built from OpenJDK, Oracle GraalVM, and a specified Oracle Java 8 build. Red Hat says the vulnerable code was introduced in OpenJDK 17.0.6; it says OpenJDK 8 and 11 are not affected. The issue also requires an x86-64 processor with AVX-512 VBMI. Red Hat says ARM64 systems and x86-64 processors without that instruction set are not affected.
Oracle’s advisory says exploitation requires data to reach the affected component through an API, for example through a web service. That makes externally supplied input relevant to the risk assessment. Oracle says untrusted Java Web Start applications and untrusted applets are not the route described in its advisory. CISA’s alert characterizes the possible outcome as remote code execution, while the precise exposure of any particular application depends on its configuration and use.
Oracle included a fix in its November 2026 Critical Patch Update. The release covers 655 new security patches across Oracle products, including 11 for Java SE; this CVE received the highest score among those Java SE issues. The OpenJDK project also published an advisory on November 17. CISA recommended immediate patching. Administrators should check Java runtimes bundled with other products and container images, as well as runtimes installed directly on servers.
Patch Java Where All Three Conditions Meet
Java is used in server applications that process data from users and other systems. A flaw in a commonly used decoder matters because Base64 data can appear in routine inputs such as tokens, cookies and uploads. If an affected runtime on a qualifying processor passes untrusted data to the vulnerable code, the outcome described by CISA could extend beyond a service crash to remote code execution.
The three conditions help narrow immediate exposure, but they do not remove the need to inventory and patch. Organizations may not know which processor features are available in each environment, and Java can be embedded inside third-party software or containers. Prioritizing internet-facing systems and checking vendor guidance can help teams identify where the fix applies.
Severity scores differ: Oracle assigns 8.1 out of 10 and calls the flaw difficult to exploit; Red Hat rates it critical at 9.8; the researchers give it 9.2 under CVSS 4.0. The National Vulnerability Database had not scored it in the supplied material. These numbers reflect different assessments and should not be treated as evidence that exploitation has occurred.
Products Worth Considering

Samsung Galaxy Tab A11+ Tablet (6GB RAM, 128GB Storage, Gray)

Logitech MX Mechanical Wireless Illuminated Keyboard, Tactile Quiet, Graphite

Apple AirPods Pro 3 Wireless Earbuds with Active Noise Cancellation
As an affiliate, we earn on qualifying purchases.
November Advisories Define the Exposure
CISA’s November 17 alert names the vulnerability, links to Oracle’s advisory and recommends actions for organizations. The Canadian Centre for Cyber Security contributed to the alert. Oracle publishes Critical Patch Updates on a quarterly schedule and says its November package complements that cycle with additional patches. OpenJDK, the open-source project on which many Java distributions are based, issued a matching advisory the same day.
The Java4Shell name echoes Log4Shell, a widely known vulnerability in a Java logging library. That resemblance is a naming choice by the finders; it does not establish that the flaws have the same technical scope or impact. Here, the supplied advisories describe a specific decoder issue with processor and runtime limits.
The record status in the source material is time-bound: CISA’s CVE data listed “Exploitation: none” on November 17, and the flaw was absent from CISA’s known exploited vulnerabilities catalogue version dated November 18. Those records describe what had been reported at those dates, not a guarantee about later activity.
““strongly urges organizations to immediately patch””
— CISA
Exploitation Status May Change
As of the dates cited, CISA’s record reported no exploitation and the vulnerability was not listed in its known exploited vulnerabilities catalogue. That does not establish whether attempts began after those records were checked. The supplied material does not identify affected organizations, confirmed compromises or observed attacks.
The sources also do not establish how many systems meet all three exposure conditions. A Java version alone cannot determine whether a service is vulnerable: processor support and whether external data reaches the decoder also matter. The researchers said they were withholding product-specific attack chains until users had time to upgrade, leaving those details outside the available material.
Install Vendor November Updates
Administrators should identify Java runtimes in use, including those bundled with applications and container images, then apply the relevant vendor’s November 2026 update. Organizations can begin with internet-facing services and confirm runtime and processor details against vendor advisories. CISA’s alert and the vendor notices are the references for product-specific remediation.
Security teams should watch for revised vendor guidance and updates to CISA’s exploitation records as reporting develops. The supplied sources do not give a later milestone or deadline beyond CISA’s call for immediate patching.
Key Questions
What is Java4Shell?
It is the name used by the flaw’s finders for CVE-2026-114938, a memory-corruption vulnerability in an optimized Base64 decoder in the Java HotSpot JVM.
Which Java versions are affected?
The advisories identify Java 17, 21, 25 and 27 runtimes, Oracle GraalVM, and a specified Oracle Java 8 build. Red Hat says OpenJDK 8 and 11 are not affected. Check the relevant vendor advisory for the exact build.
Does every system running an affected Java version have the flaw?
No. The described exposure also requires an x86-64 processor with AVX-512 VBMI and an application path that supplies data to the affected decoder. Red Hat says ARM64 and x86-64 systems without that processor feature are not affected.
Has Java4Shell been exploited?
CISA’s CVE record listed no exploitation on November 17, 2026, and the flaw was not in the agency’s known exploited vulnerabilities catalogue version dated November 18. Those dated records do not confirm its status after those checks.
Should organizations patch Java?
Yes. CISA urged immediate patching, and Oracle and OpenJDK published November 2026 fixes. Organizations should check directly installed runtimes as well as Java bundled with products and container images.
Source: Thorsten Meyer AI