TL;DR

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Microsoft has released a large-scale security update patching over 570 vulnerabilities across its software products. This update aims to improve security and protect users from potential exploits. The full scope and severity levels are still being assessed.
Microsoft has released a series of software updates that patch at least 570 security vulnerabilities across its product portfolio, including Windows operating systems and Office applications. The updates aim to strengthen security defenses amid increasing cyber threats, affecting millions of users worldwide.
The updates, issued on March 2024, address a broad range of security flaws, with some classified as critical or high severity. Microsoft confirmed that these patches cover vulnerabilities that could allow remote code execution, privilege escalation, or data theft, potentially enabling cybercriminals to compromise affected systems.
Microsoft’s security team emphasized that the updates are part of its regular Patch Tuesday cycle but constitute one of the largest vulnerability fixes in recent months. The company recommends that all users and organizations apply these updates promptly to mitigate risks.
Implications for Cybersecurity and User Safety
This extensive update underscores the persistent and evolving nature of cybersecurity threats targeting Microsoft products. By patching over 570 vulnerabilities, Microsoft aims to reduce the risk of cyberattacks that could exploit these flaws, safeguarding sensitive data and maintaining system integrity. For users and organizations, timely application of these patches is critical to prevent potential breaches and cyber incidents.
Products Worth Considering

EcoFlow Smart Home Panel 2 Whole-Home Backup System Hub
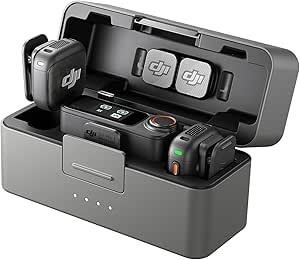
DJI Mic 3 Wireless Microphone System (2 Transmitters, 1 Receiver, Charging Case)

Bose QuietComfort Wireless Bluetooth Headphones with Active Noise Cancellation, Mic, USB‑C Charging, Deep Bass, 24‑Hour Battery – White Smok
As an affiliate, we earn on qualifying purchases.
Recent Trends in Microsoft Security Patches
Microsoft regularly releases security updates as part of its Patch Tuesday cycle, typically addressing dozens of vulnerabilities each month. However, this latest update is notable for its volume, reflecting the increasing complexity and number of security flaws discovered in widely used software. Past incidents, such as the widespread exploitation of certain vulnerabilities, have heightened awareness of the importance of prompt patching.
Security researchers have identified a rise in targeted attacks exploiting unpatched Microsoft vulnerabilities, prompting the company to accelerate its response efforts. The current update follows reports of emerging exploits and ongoing threat campaigns targeting Windows and Office users.
“This update addresses a significant number of vulnerabilities that could be exploited by attackers. We strongly recommend that users apply these patches as soon as possible.”
— Microsoft Security Response Center
Details on Vulnerability Severity and Exploitation
While Microsoft has confirmed the total number of vulnerabilities patched, the specific severity levels of many flaws and the extent to which they are currently being exploited in the wild remain unclear. Microsoft has not disclosed detailed information on which vulnerabilities are actively targeted by cybercriminal groups.
Monitoring and Future Security Updates
Microsoft is expected to monitor the effectiveness of these patches and release additional updates if new vulnerabilities are discovered. Organizations should continue to follow security advisories and implement best practices for system updates. Researchers and cybersecurity firms will likely analyze these patches for indications of emerging threat patterns.
Key Questions
Which Microsoft products are affected by these updates?
The updates cover a wide range of Microsoft products, including Windows operating systems, Microsoft Office, Edge browser, and other enterprise services.
How critical are these vulnerabilities?
Microsoft has classified some vulnerabilities as critical or high severity, indicating they could allow remote code execution or significant privilege escalation if exploited.
What should users do to stay protected?
Users and organizations should promptly apply the latest security updates through Windows Update or their management systems to mitigate risk.
Are there known exploits for these vulnerabilities?
Microsoft has not confirmed widespread active exploits for all vulnerabilities, but some may be targeted by attackers. Continuous monitoring and prompt patching are advised.
Source: hn