Most teams overlook that access permissions often stay static after onboarding, creating security gaps over time. You might forget to regularly review or update permissions, leaving users with unnecessary access. Manual processes and neglecting audits increase the risk of insider threats and data breaches. This makes your organization vulnerable to evolving threats and role changes. Staying proactive and implementing automated tools can help you close these gaps—keep going to learn more about how to strengthen your SaaS identity security.

Get privacy and security gear delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
Key Takeaways
- Teams often overlook the importance of regular access reviews and timely permission updates.
- Many fail to implement continuous monitoring of user activity for anomalies.
- Relying solely on manual processes increases human error and oversight in managing permissions.
- Insufficient enforcement of least privilege principles leaves security gaps.
- Organizations neglect ongoing audits and policy updates to adapt to evolving threats.
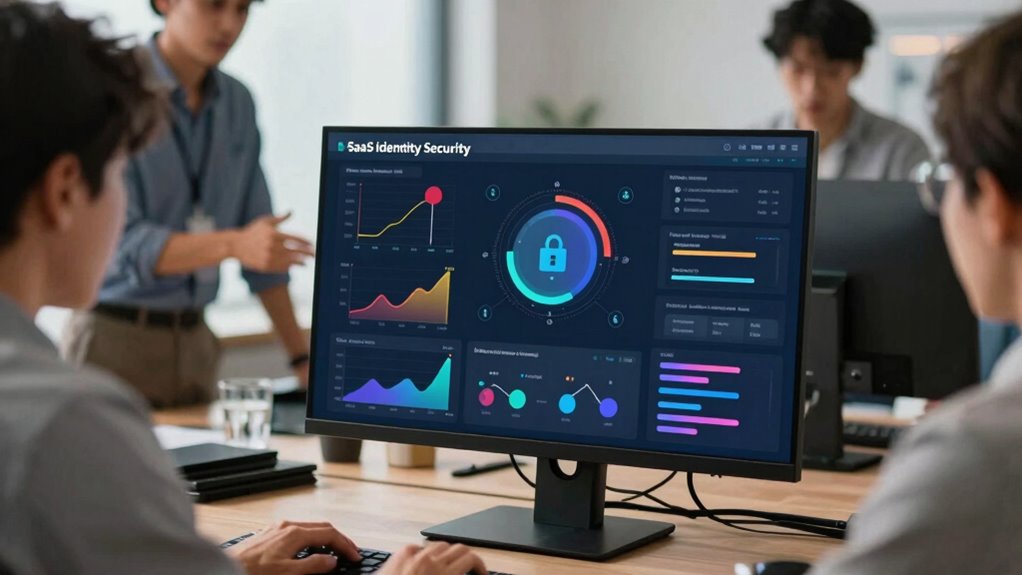
Beyond onboarding, access management is often underappreciated. You might think that once someone is inside your SaaS environment, their access stays consistent, but the reality is much more dynamic. Without robust access management, users may retain permissions they no longer need, or access sensitive data beyond their scope. That’s a common oversight—failing to regularly review and update permissions. Automated tools can help, but many teams still rely on manual processes or neglect ongoing audits altogether. This oversight can lead to security vulnerabilities, especially if employees change roles or leave the company. Proper access management means implementing least privilege principles, enforcing multi-factor authentication, and continuously monitoring user activity to detect anomalies. Recognizing identity security as an ongoing process is essential for adapting to evolving threats and maintaining a strong security posture. Regularly conducting security audits and updating policies can significantly reduce the risk of insider threats and external breaches. Additionally, integrating automated access reviews can streamline the process and reduce human error, ensuring permissions are always aligned with current roles.
SaaS identity management software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Frequently Asked Questions
How Often Should Saas Identity Security Policies Be Reviewed?
You should review your SaaS identity security policies at least quarterly to stay ahead of evolving threats. Regular policy updates ensure they remain effective, and incorporating user training keeps your team aware of best practices. Frequent reviews help identify vulnerabilities early, allowing you to implement necessary changes promptly. This ongoing process minimizes risks, guarantees compliance, and promotes a security-conscious culture across your organization.
What Are the Signs of a Compromised Saas Identity System?
Think of your SaaS identity system like a security guard; if you notice unauthorized user access or unusual activity, it’s a sign of trouble. Signs of a compromised system include unexpected login locations, rapid credential theft, or multiple failed login attempts. If user access suddenly spikes or if users report suspicious activity, these are red flags indicating your credentials might be compromised. Stay vigilant; quick detection can prevent major breaches.
How Can Small Teams Effectively Implement Saas Identity Security?
To effectively implement SaaS identity security, focus on strengthening user authentication and access management. Use multi-factor authentication to verify user identities and set strict access controls based on roles. Regularly review permissions to prevent privilege creep, and monitor login activities for suspicious behavior. Educate your team on security best practices, and automate security policies where possible to minimize human error, ensuring your SaaS environment stays protected.
What Are Emerging Threats to Saas Identity Security in 2023?
In 2023, over 80% of organizations face rising threats, especially from phishing attacks and credential breaches. You need to stay alert as cybercriminals increasingly target SaaS identities, exploiting weak links. Emerging threats include sophisticated spear-phishing campaigns and automated credential stuffing. You must implement multi-factor authentication and continuous monitoring to defend against these evolving risks. Staying proactive is essential to safeguarding your SaaS environment from these growing security threats.
How Does Saas Identity Security Differ Across Industries?
You’ll notice SaaS identity security varies across industries because each requires industry-specific authentication methods to address unique risks. For example, healthcare demands stricter regulatory compliance, impacting access controls and data handling. Financial services implement rigorous multi-factor authentication, while retail emphasizes seamless user experiences. Understanding these differences helps you tailor security measures effectively, ensuring compliance and protecting sensitive data while maintaining operational efficiency across diverse sectors.
multi-factor authentication devices
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Conclusion
So, here’s the irony: while you scramble to patch every security hole and tighten access, you might overlook the simplest mistake—assuming your SaaS identity security is foolproof. It’s almost poetic how, in trying to outsmart cyber threats, you forget that human error and complacency are often the biggest vulnerabilities. Remember, the most overlooked security measure could be your own team’s password habits or outdated policies. Sometimes, the biggest risk is the one you’re too confident to see.
As an affiliate, we earn on qualifying purchases.
user activity monitoring software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.