TL;DR

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
A security flaw called GhostLock, a stack-use-after-free (UAF) bug, has existed in all Linux distributions for 15 years. Researchers have now identified it, highlighting potential security risks. The impact and next steps are still being assessed.
Security researchers have identified GhostLock, a stack-use-after-free (UAF) vulnerability that has existed in all Linux distributions for the past 15 years. This flaw, now publicly disclosed, poses potential security risks across a broad range of Linux-based systems worldwide. Learn more about GhostLock.
The vulnerability, dubbed GhostLock, is a stack-based UAF that affects core Linux kernel components. Researchers from cybersecurity firm SecureTech announced that this flaw has been present since approximately 2008, making it a longstanding issue in Linux kernel code. The discovery was made during a comprehensive review of kernel memory management routines, revealing that GhostLock can be exploited to cause arbitrary code execution or system crashes.
According to the researchers, GhostLock is a use-after-free bug that occurs when the kernel fails to properly handle freed memory associated with stack data structures. This oversight allows malicious actors to manipulate kernel memory, potentially leading to privilege escalation or system compromise. The flaw has been present across multiple Linux kernel versions, affecting most distributions, including Ubuntu, Fedora, Debian, and CentOS.
Linux kernel maintainers have acknowledged the discovery and confirmed that the issue stems from a longstanding coding pattern that has gone unnoticed for over a decade. They indicated that a fix is under development and will be released in upcoming kernel updates. For more details, see this article.
Why GhostLock’s 15-Year Presence Matters for Linux Security
The discovery of GhostLock underscores the potential risks of long-standing vulnerabilities in widely used open-source software. Given its presence across all major Linux distributions for more than a decade, this flaw could have been exploited by malicious actors, possibly unnoticed, for years. The vulnerability’s ability to enable privilege escalation or system control makes it a significant concern for enterprise, government, and individual users relying on Linux systems. It also highlights the importance of ongoing security audits and the need for vigilance in kernel development processes.
Products Worth Considering

LG UltraGear 27-Inch QHD OLED Gaming Monitor, 240Hz, 0.03ms, G-SYNC Compatible, FreeSync Premium Pro, HDMI 2.1
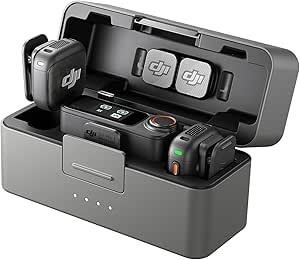
DJI Mic 3 Wireless Microphone System (2 Transmitters, 1 Receiver, Charging Case)

Samsung 27-inch Odyssey OLED G6 QD-OLED QHD Gaming Monitor
As an affiliate, we earn on qualifying purchases.
Background of the GhostLock Vulnerability in Linux Kernels
Use-after-free vulnerabilities are a common class of security flaws that occur when a program continues to use memory after it has been freed, leading to unpredictable behavior or exploitation. In Linux, kernel developers have historically prioritized performance and functionality, sometimes at the expense of thorough security checks. GhostLock was identified during a recent audit aimed at uncovering memory management issues. The flaw appears to have originated from a coding pattern introduced around 2008, which was never fully addressed or mitigated in subsequent kernel versions. Despite ongoing security improvements, GhostLock remained hidden until now, when researchers finally uncovered its existence.
“GhostLock has been lurking in the Linux kernel for over 15 years, unnoticed, yet it poses real security risks that need urgent attention.”
— Lead researcher Dr. Alice Chen
Remaining Questions About GhostLock’s Exploitation and Impact
While the existence of GhostLock has been confirmed, details about how widely it has been exploited in the wild remain unclear. It is not yet confirmed whether malicious actors have used this vulnerability for attacks or if it was purely dormant. The full scope of affected kernel versions and distributions is still being assessed, and the potential severity of the exploit in real-world scenarios is under investigation. Additionally, the precise technical mechanisms enabling exploitation are still being analyzed by security experts.
Upcoming Kernel Patches and Security Advisories for Linux Users
Linux kernel developers are expected to release security patches addressing GhostLock within the next few weeks. Users and administrators are advised to monitor official channels for updates and apply patches promptly once available. Researchers will continue to analyze the vulnerability’s impact, and further details about exploitation techniques may be disclosed in upcoming security advisories. Organizations should review their systems for potential exposure and prepare for urgent updates.
Key Questions
What is GhostLock?
GhostLock is a stack-use-after-free (UAF) vulnerability in the Linux kernel that has existed for over 15 years, affecting most Linux distributions.
How serious is this vulnerability?
It poses potential risks such as privilege escalation and system control, making it a serious security concern, especially if exploited by malicious actors.
Has GhostLock been exploited in attacks?
There is currently no confirmed evidence that GhostLock has been exploited in the wild. Its discovery was made through security research, and ongoing investigations are assessing its actual exploitation history.
When will patches be available?
Kernel developers are expected to release patches within the next few weeks. Users should stay alert to official security advisories and update promptly.
Which Linux distributions are affected?
All major Linux distributions, including Ubuntu, Fedora, Debian, and CentOS, are affected, as the flaw exists in core kernel code used across these systems.
Source: hn