When engineers get involved early, security becomes part of the development process, helping you find potential vulnerabilities before they become costly problems. You can implement protective measures, align teams, and avoid misunderstandings that cause delays later. Early involvement encourages a security-first mindset and makes your system more resilient from the start. This proactive approach not only saves time and resources but also strengthens your product’s overall security—discover how this can transform your workflow if you keep exploring.

Get privacy and security gear delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
Key Takeaways
- Early engineer involvement identifies vulnerabilities before integration, reducing security issues later.
- It fosters better communication, aligning security goals from the project’s start.
- Proactive security measures create more resilient systems, minimizing breach risks.
- Engineers’ early participation promotes a security-first culture, preventing rushed compromises.
- Continuous security input during development streamlines reviews and reduces costly late fixes.
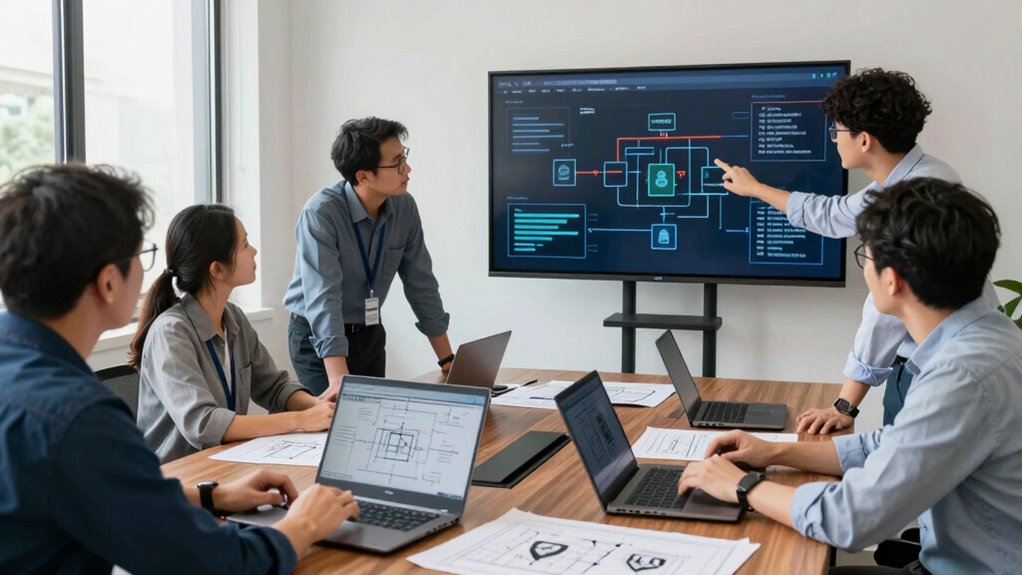
Integrating engineers into the security review process early in development leads to more effective and efficient outcomes. When you involve engineers from the outset, you can identify potential vulnerabilities during the code integration phase, rather than discovering them after considerable development has occurred. This proactive approach minimizes the risk of security flaws slipping through, saving valuable time and resources down the line. Early collaboration allows you to embed security best practices directly into the development process, ensuring that security considerations are not an afterthought but an integral part of the product’s foundation.
Early developer involvement in security reviews ensures proactive vulnerability identification and integrated security best practices.
As you bring engineers into the security review early, you enable a more seamless flow of communication between development and security teams. This alignment helps clarify the security requirements and objectives right from the start, reducing misunderstandings and rework. When security reviews happen later in the development cycle, you often face complex, costly fixes due to late-stage code changes. But by addressing security concerns during code integration, you can implement incremental improvements that are easier and less disruptive. This iterative process also encourages developers to adopt a security-first mindset, making it more natural to write secure code from the beginning. Incorporating security best practices early on helps create a stronger foundation for the entire development lifecycle.
Early engagement in security reviews notably enhances threat mitigation. You gain the opportunity to identify and address potential attack vectors before they become critical issues. This foresight enables you to design more resilient systems, reducing the likelihood of breaches and data leaks. When engineers understand the security implications of their code early, they can incorporate protective measures—like input validation, proper authentication, and secure data handling—during development. The result is a product that’s inherently more secure, with fewer vulnerabilities that need patching after deployment. Emphasizing security considerations throughout the process ensures a more comprehensive security posture from the outset.
Furthermore, involving engineers early in security reviews fosters a culture of shared responsibility. When everyone understands the importance of security from the start, you’re more likely to see consistent adherence to security standards throughout the development process. It also helps prevent the temptation to cut corners just to meet deadlines, as security becomes a natural part of the workflow. As a result, you reduce the likelihood of security gaps caused by rushed or incomplete code, ultimately delivering a safer and more reliable product.
As an affiliate, we earn on qualifying purchases.
Frequently Asked Questions
How Early Should Engineers Be Involved in Security Reviews?
You should involve engineers in security reviews as early as possible, ideally during the initial design phase. This allows them to participate in security training and understand potential risk assessments from the start. Early involvement helps identify vulnerabilities early, reducing costly fixes later. By integrating security into the development process, you guarantee a more secure product, and engineers become more aware of security best practices from the outset.
What Specific Security Risks Are Mitigated by Early Engineering Involvement?
Getting engineers involved early is like catching a problem before it blooms. You’ll mitigate vulnerabilities by engaging in threat modeling from the start, identifying potential weak spots before they become security holes. This proactive approach helps you address security risks early, reducing the chances of costly fixes later. Overall, early involvement guarantees threats are managed efficiently, transforming security from a reactive chore into a strategic advantage.
How Does Early Participation Affect Project Timelines and Budgets?
Early participation speeds up project timelines and controls budgets by integrating security compliance and risk assessment from the start. When you involve engineers early, you identify potential security issues early, reducing costly revisions later. This proactive approach minimizes delays and prevents budget overruns caused by late-stage fixes. Ultimately, it guarantees that security considerations are woven into the project seamlessly, saving time and money while maintaining strong security standards.
Are There Any Drawbacks to Involving Engineers Early in Security Reviews?
While involving engineers early in security reviews enhances security training and guarantees compliance checks are integrated from the start, it can also slow down progress initially. You might face increased meetings and adjustments, which could lead to frustration or delays. However, these drawbacks often outweigh the benefits, as early involvement reduces costly rework later, improves security awareness, and guarantees compliance — ultimately strengthening your project’s security foundation.
How Can Organizations Encourage Engineers to Prioritize Security Early?
You can encourage engineers to prioritize security early by fostering security awareness through regular training and discussions. Emphasize the importance of risk assessment in their daily tasks, making security a shared responsibility. Recognize and reward proactive security contributions to motivate engagement. When engineers see how security impacts project success, they’re more likely to integrate best practices from the start, reducing vulnerabilities and streamlining security reviews.
developer security training courses
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Conclusion
When you join security reviews early, you catch issues sooner, build better security habits, and foster stronger collaboration. Early involvement means fewer surprises, clearer communication, and more effective solutions. It’s about preventing problems before they grow, aligning team efforts from the start, and creating a culture of security-minded thinking. When you prioritize early engagement, you empower your team, improve your product, and guarantee security becomes a shared responsibility—making the entire process smoother, safer, and more successful.
application security testing software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
security vulnerability scanners for developers
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.