TL;DR

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Security researchers have discovered a vulnerability that allows malicious actors to exploit System Management Mode (SMM) using very long interrupts. This could enable privilege escalation and hardware-level attacks. The flaw’s full impact and mitigation strategies are still under investigation.
Security researchers have revealed a vulnerability that allows attackers to exploit System Management Mode (SMM) using very long interrupts, potentially enabling privilege escalation at the hardware level. This discovery raises concerns about the security of modern processors and firmware, as the flaw could be exploited to bypass existing protections.
The vulnerability was identified by a team of security researchers who demonstrated that malicious actors could trigger prolonged interrupts, which in turn could manipulate the behavior of SMM. SMM is a high-privilege mode used for low-level hardware management, and exploiting it could allow an attacker to execute arbitrary code with system-wide privileges.
According to the researchers, the attack involves sending specially crafted interrupt requests that exceed typical handling durations, causing SMM to behave unexpectedly. This could lead to data leakage, system crashes, or the execution of malicious firmware code. The researchers have not yet disclosed specific hardware models affected, but the flaw appears to be related to how interrupt handling is implemented in certain CPU architectures.
Potential Impact on Hardware Security and Data Integrity
This vulnerability is significant because System Management Mode operates at a high privilege level, isolated from the operating system and hypervisors. Exploiting SMM could allow attackers to bypass security controls, access sensitive data, or even persist malicious code at the firmware level. Given the critical role of SMM in hardware management, this flaw could have widespread implications for enterprise and consumer systems alike.
Products Worth Considering

EcoFlow Smart Home Panel 2 Whole-Home Backup System Hub
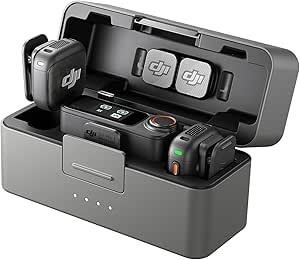
DJI Mic 3 Wireless Microphone System (2 Transmitters, 1 Receiver, Charging Case)

Apple iPad Air (2025) 13‑inch Wi‑Fi 256 GB – Space Gray (M3 chip)
As an affiliate, we earn on qualifying purchases.
Recent Discoveries in Hardware Security Vulnerabilities
Hardware security vulnerabilities involving low-level firmware and privilege modes have been a focus of research in recent years, with notable examples like Spectre and Meltdown highlighting the risks of processor-level flaws. The current discovery adds to this trend by exposing a new attack vector through the manipulation of interrupt handling in System Management Mode. The research team published their findings in a preliminary report, but detailed technical specifics are yet to be released.
Extent of Affected Hardware and Exploitability
It is not yet clear which specific CPU models or firmware implementations are vulnerable, nor has a practical exploit been publicly demonstrated. Researchers are still investigating the full scope of the flaw and its potential for widespread abuse. Additionally, the effectiveness of existing mitigations remains uncertain.
Expected Steps Toward Mitigation and Disclosure Timeline
Further technical details are expected to be published by the researchers in the coming weeks. Hardware manufacturers and firmware developers are likely to evaluate their systems for this vulnerability and develop patches or mitigations. Regulatory agencies and security organizations may issue advisories once the scope and exploitability are better understood.
Key Questions
How does exploiting long interrupts affect system security?
Exploiting long interrupts can manipulate the behavior of System Management Mode, potentially allowing attackers to execute malicious code with high privileges, bypassing security controls.
Are all processors vulnerable to this flaw?
It is currently unknown which specific hardware models are affected. The vulnerability appears related to certain implementations of interrupt handling in CPU architectures, but detailed scope is still under investigation.
Can this vulnerability be mitigated with software updates?
Potential mitigations may involve firmware patches or configuration changes, but the effectiveness of software-only solutions is still being evaluated. Hardware-level fixes may be necessary for full mitigation.
When will more technical details be available?
The research team plans to publish a detailed technical report in the coming weeks, which should clarify the scope and exploitability of the flaw.
What should organizations do now?
Organizations should monitor updates from hardware vendors and security agencies, and prepare to apply patches once available. Increased vigilance around firmware security is advised.
Source: hn